 TempLogin
Authentication
The alpha uses email possession and a one-time link. Authenticator-based MFA, enrolment and recovery are future implementation. A second message to the same inbox will not be called independent 2FA.
TEMPORARY WORDPRESS ACCESS, EXPLAINED
From the first invitation to the last session, TempLogin is being built around a clear relationship between the person, their permissions and their approved time.
See current alpha scope ↗Product direction · Individual features below distinguish alpha implementation from future development.
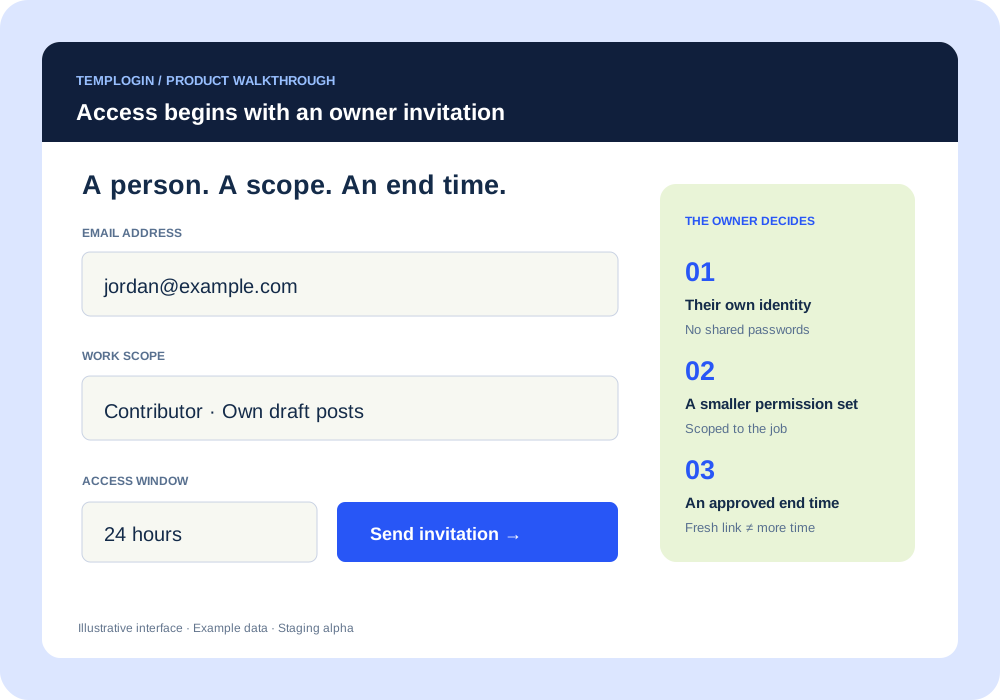
01 / INVITATIONS
The owner starts every first-time engagement. An email address identifies the invitee; the approved grant sets the permissions and end time. Existing permanent accounts are kept separate.
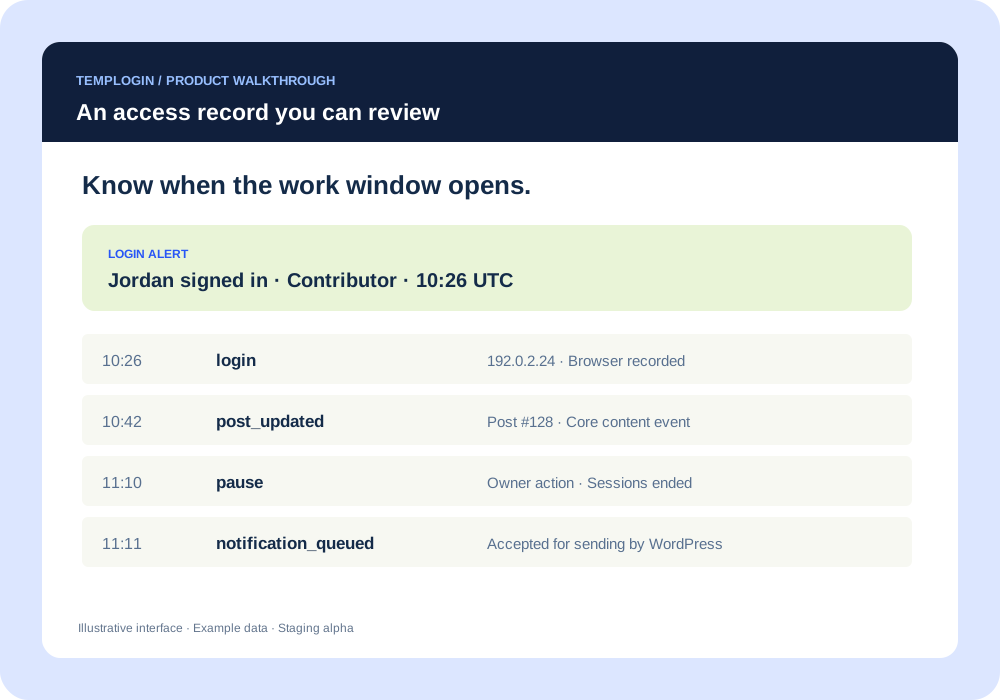
02 / VISIBILITY & CONTROL
See when a temporary person signs in and review supported access and content events. Pause or close the grant when the engagement changes.
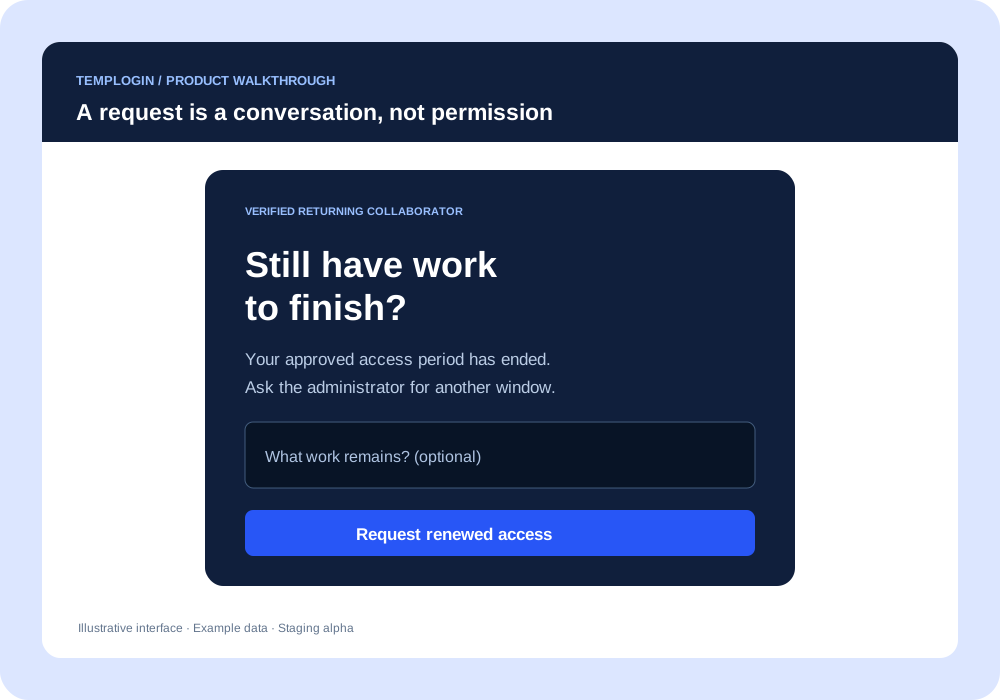
03 / RENEWAL
Previously approved collaborators may have work left to do. Verification and a real grant history come before a renewal request. Pending requests never create permissions.
SECURITY & GOVERNANCE
Login safety belongs in the free core. Paid value comes from coordination, scale and organisation policy.
The alpha uses email possession and a one-time link. Authenticator-based MFA, enrolment and recovery are future implementation. A second message to the same inbox will not be called independent 2FA.
Business will add permission templates, vendor records, approval routing, maintenance windows and detailed reports. These are proposed features, not alpha capabilities.
Enterprise will add mandatory policies, independent approvals, access reviews and external evidence. These can support security processes; they do not certify a site or an organisation.
Review the proposed editions and tell us what your handovers need.